Document security · Enterprise & Government
Every document you issue.
Verified. Tamper-evident.
DocSec issues tamper-evident official documents and professional credentials — and ingests finalized documents from legacy repositories for cryptographic signing and real-time public verification.
AES-256
Encryption at rest
TLS 1.3
Enforced in transit
ISO 27001
Certified cloud infrastructure
3 years
Immutable audit logs
Why DocSec
One platform for the integrity of every credential
Issue with certainty
Every document you issue carries a tamper-evident QR code sealed with a SHA-256 verification key. The slightest change to that key fails verification instantly.
Verify in seconds
Anyone can scan and confirm a credential in real time — no phone calls, no manual auditing. Institutions can even set their own verification fees for third parties.
Govern at scale
Role-based access control, departmental licences and a three-year immutable audit trail give institutions full authority over every user, document and action.
How it works
From registration to verification
- 01
Register your institution
Your Key User becomes the System Administrator — free of charge — with global authority over the instance, verification fees and departmental licences.
- 02
Provision departments
Add each office or department under an annual licence. Its first user becomes Department Admin — managing issuance templates, user permissions and both native generation and legacy document ingestion.
- 03
Issue or ingest documents
Generate transcripts, licences, certificates and land titles natively — or ingest finalized documents from legacy EDMS repositories — each sealed with its own encrypted, tamper-evident QR key.
- 04
Verify anywhere
Third parties scan the QR code to confirm authenticity in real time — reducing fraud, manual audits and verification backlogs.
The platform
Built for the way institutions actually work
A responsive, WCAG-conscious interface over a strictly-typed, service-oriented backend — with RESTful APIs secured by JWT, isolated instances per customer, and enterprise database options including self-hosted deployment for data sovereignty.
- Laravel 13 / PHP 8.4 strictly-typed backend on Azure or DigitalOcean
- React frontend with encrypted client-side state
- EDMS connectors to ingest documents from SharePoint, Laserfiche and Microsoft 365
- Cloudinary CDN, Paystack and stablecoin settlement support
Security & compliance
Security that fails closed
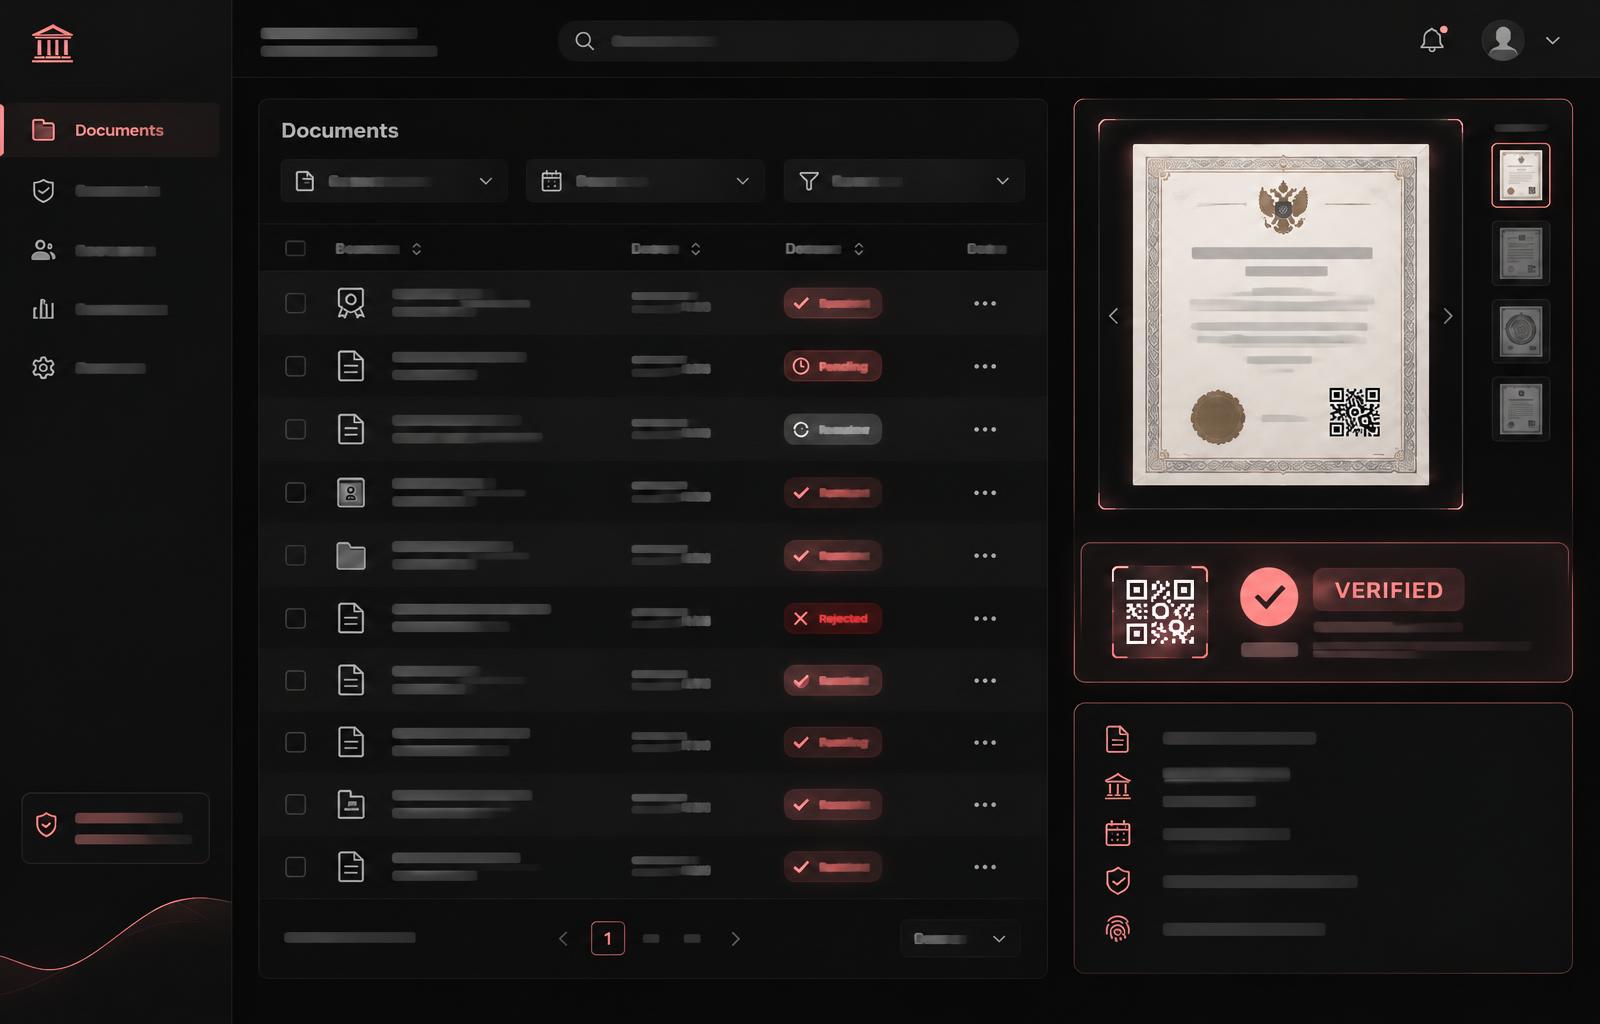
Document verification fails on the slightest change to a verification key. AES-256 encryption at rest, TLS 1.3 in transit, SSO with SAML 2.0 and Azure AD, granular RBAC, and immutable audit logs retained for three years.
Review our securitySHA-256
Encrypted QR verification keys
Multi-AZ
Zone-redundant HA infrastructure
SOC 2 Type II
Certified cloud infrastructure
RBAC + SSO
SAML 2.0, AD FS, Okta, Azure AD
Commercials
Predictable costs, revenue built in
Issuance units
Volume-tiered from $1.00 down to $0.50 per issued document as annual volume grows.
Verification revenue
Set your own third-party verifier fees. DocSec's commission drops from 30% to 15% past 500 paid checks per month.
Departmental licences
Annual licences per department — Starter at $7,500, scaling per user through Growth, Scale and Enterprise tiers.
Ready to secure every document your institution issues?
Book a demo with our team, or start free as your institution's Key User.
Request a demo